The short version
What matters most
- Use the manufacturer advisory to confirm exact affected models and versions.
- Prioritise equipment that is directly reachable from the internet or connected to sensitive networks.
- Check for signs of compromise before assuming that installing a patch ends the incident.
- Keep an asset register and advisory process so the next assessment is faster.
Confirm what the advisory actually covers
Start with the original manufacturer advisory rather than a social post or a shortened headline. Record the vulnerability identifier, affected product families, affected firmware ranges, fixed versions, known exploitation and any temporary mitigation.
Compare that information with a reliable site inventory. A similar product name is not enough: the exact model, hardware revision and installed software determine whether a device falls inside the affected range.
Practical pointDo not apply firmware mentioned in a third-party article without checking the manufacturer page for the exact device.
Work out where the greatest exposure sits
The same vulnerability can present very different risk at two sites. A device exposed directly to the internet, reachable from a broad corporate network or using shared administrator credentials deserves quicker attention than an isolated device on a tightly controlled security network.
Review remote-access routes, firewall rules, port forwarding, cloud connections and the network paths available from the affected system. Where practical, remove unnecessary exposure or isolate the equipment while the permanent response is prepared.
- Do not make cameras or recorders directly internet-facing for convenience.
- Restrict management access to authorised networks and users.
- Disable services and accounts that are not required.
- Treat shared or unchanged default credentials as an urgent separate issue.
Check whether anything happened before the fix
Patching closes the known weakness, but it does not remove access an attacker may already have gained. Review available device, recorder, firewall and remote-access logs for unusual connections, new users, configuration changes, disabled recording or unexpected reboots.
If compromise is suspected, preserve the available evidence and use the organisation’s incident process. Avoid making broad changes that overwrite logs before the security team or incident-response provider has assessed them.
Apply the manufacturer response as controlled change
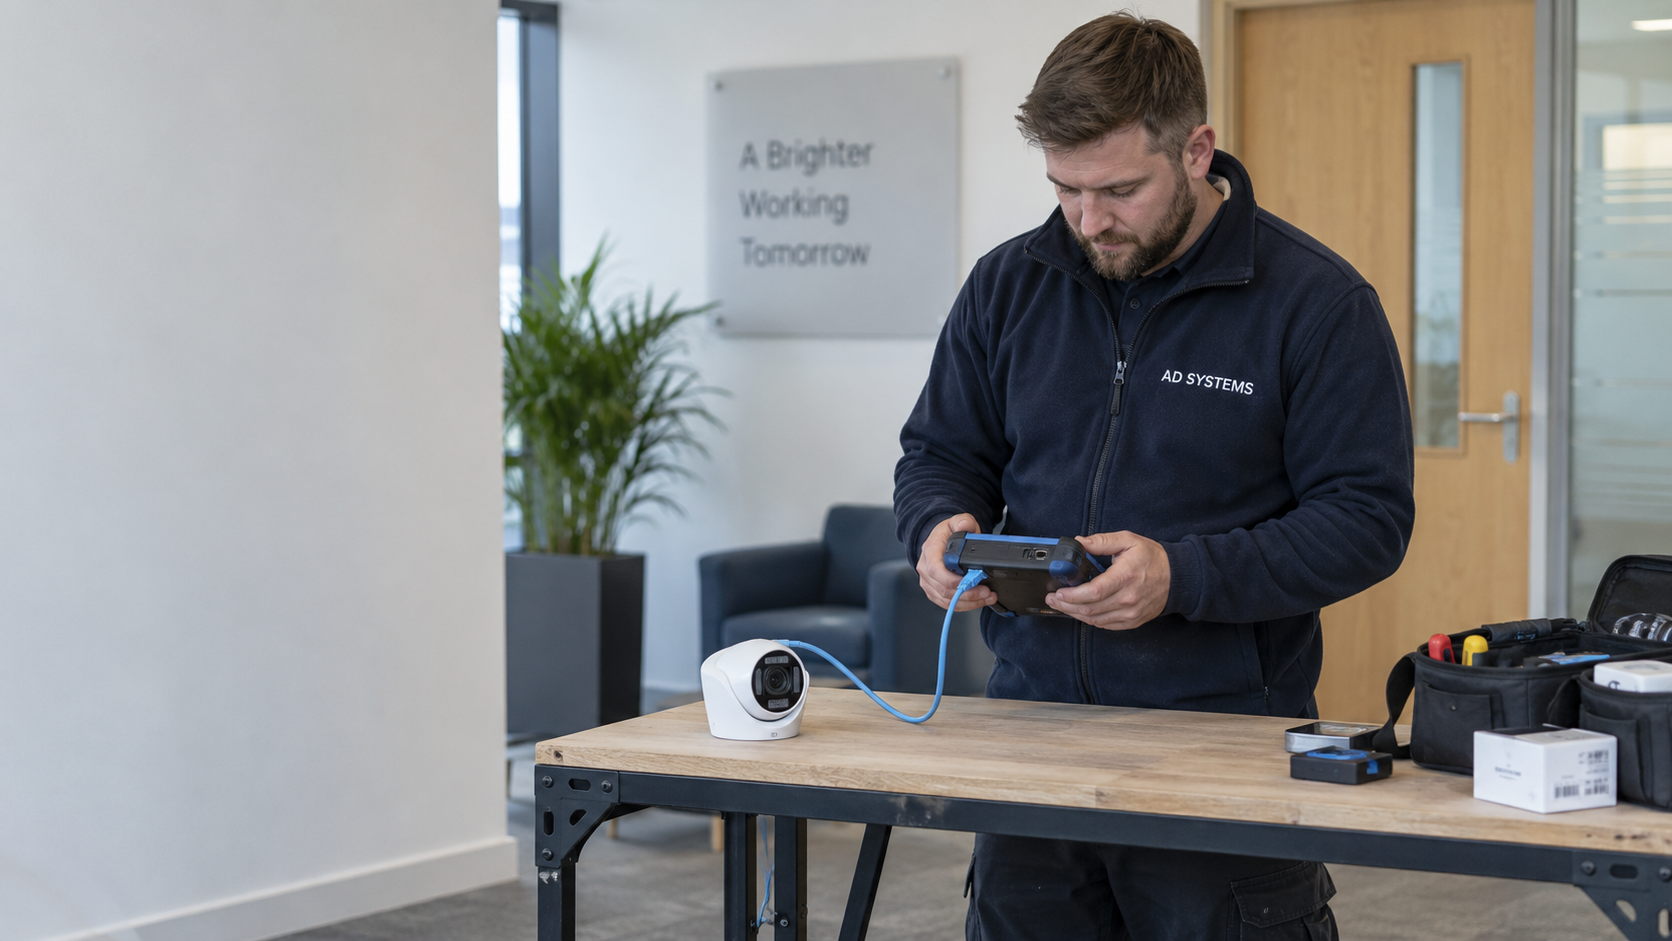
Follow the vendor’s fixed version and upgrade route. Back up the configuration, pilot the update on a representative device and verify recording, playback, alerts, integrations and remote access before continuing across the estate.
After the update, change credentials if the advisory, exposure or investigation indicates they may have been at risk. Confirm that old services, temporary firewall rules and maintenance accounts have not been left enabled.
Make the next alert easier to handle
A lightweight vulnerability process is more valuable than an occasional emergency exercise. Give each security platform an owner, maintain model and firmware information, subscribe to relevant manufacturer notices and decide how quickly different levels of exposure should be reviewed.
Include ageing equipment in lifecycle planning. A device that cannot receive a vendor fix may need compensating controls in the short term and replacement within an agreed period.
This guidance is general. Check the current manufacturer instructions, release notes and your organisation’s technical and data-protection requirements before changing a live system.